PHP2Shell, eMudhra, PingCAP: one week, three security scares (opens the source in a new tab)
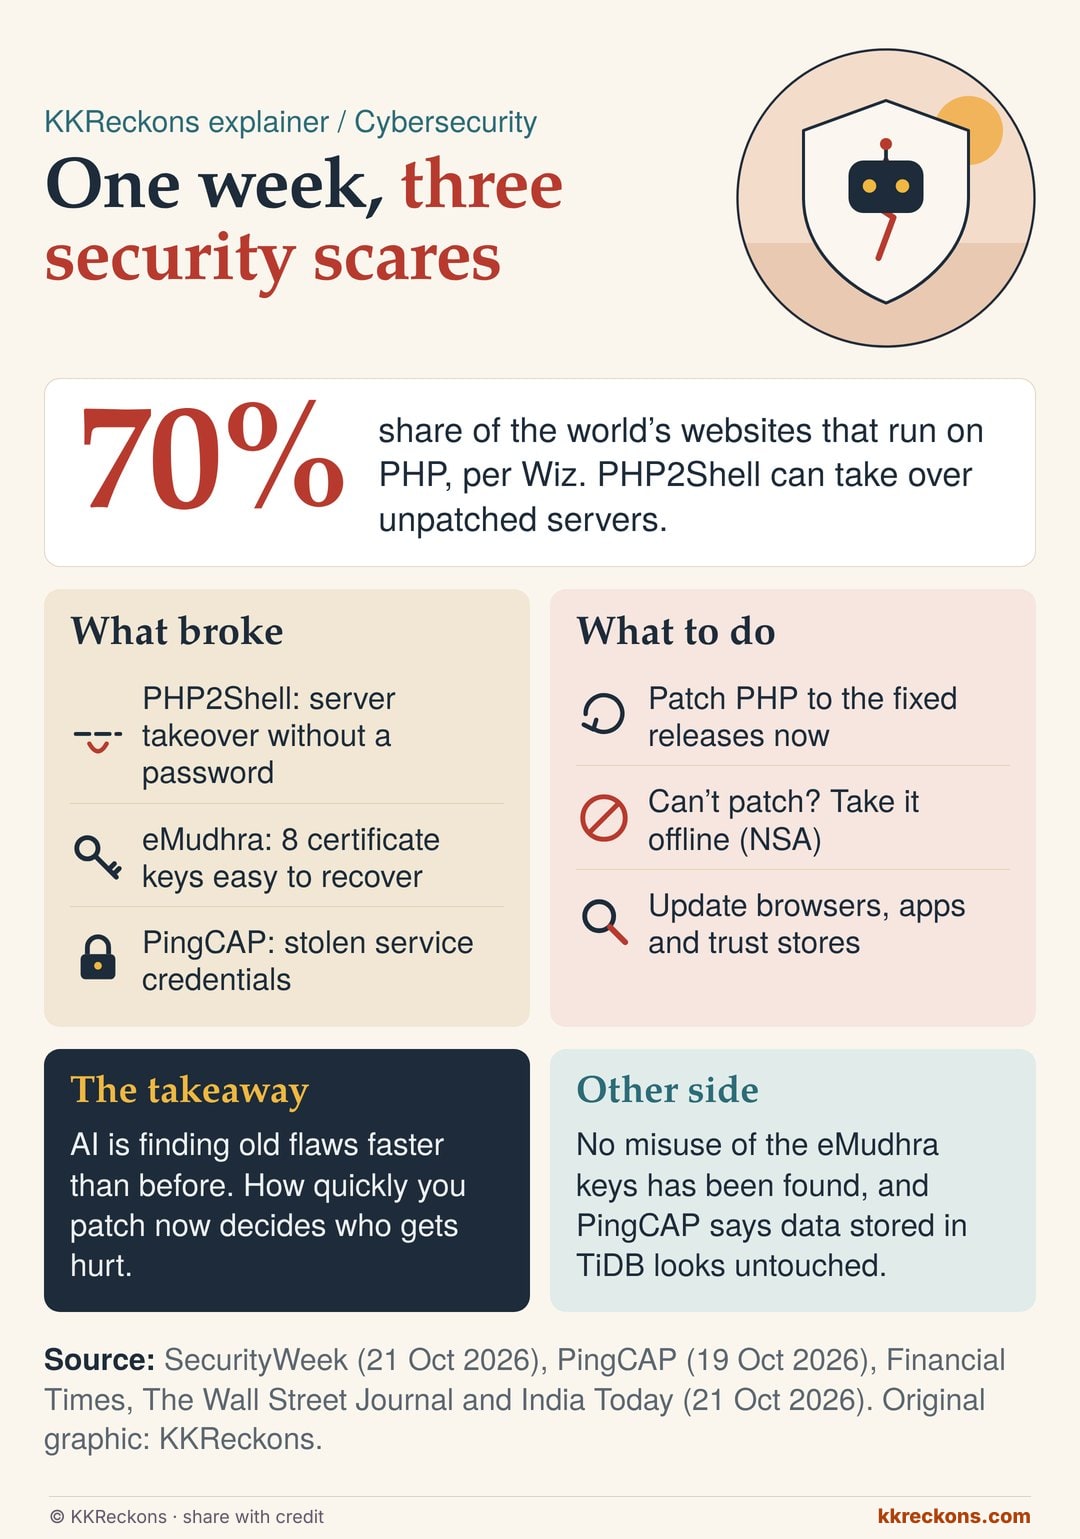
- PHP2Shell: two critical flaws (severity 9.2 of 10) let attackers take over unpatched PHP servers without a password. Found with AI help, fixes shipped on 21 Oct, a day early after a leak; Amazon says they are now broadly exploited, and the NSA says patch or go offline.
- eMudhra: eight intermediate certificates had keys weak enough to recover almost instantly. Mozilla, Google, Apple and Microsoft have blocked them; no misuse shows in public logs, and India’s IT ministry has set up a probe.
- PingCAP: stolen service credentials let an intruder copy TiDB Cloud user details, SQL editor text, billing data and encrypted API keys. It sees no sign that data stored in TiDB was hit.
- 70%
- of websites run on PHP, says Wiz
- 9.2
- PHP2Shell severity score
- 8
- eMudhra certificates blocked
Why it matters AI is now finding old flaws faster than defenders can patch them, and the weak link is often a script or a stolen password rather than exotic code.
Watch next Patch speed. Servers and apps that update slowly may show damage in the coming weeks, though so far no attack using the eMudhra keys is known.
Also read: Browsers block eMudhra intermediate CAs (SecurityWeek) · What is eMudhra and why the internet is worried (India Today) · AI just found a bug that puts up to 70% of websites at risk (WSJ) · Amazon warns the AI-found flaws are being broadly exploited (FT)