CERT-In flags 'critical' AI-driven attacks on Indian banks, NBFCs and fintechs (opens the source in a new tab)
Follow-up to AI is speeding up hacks. Are banks in India and abroad ready? · 5 Nov
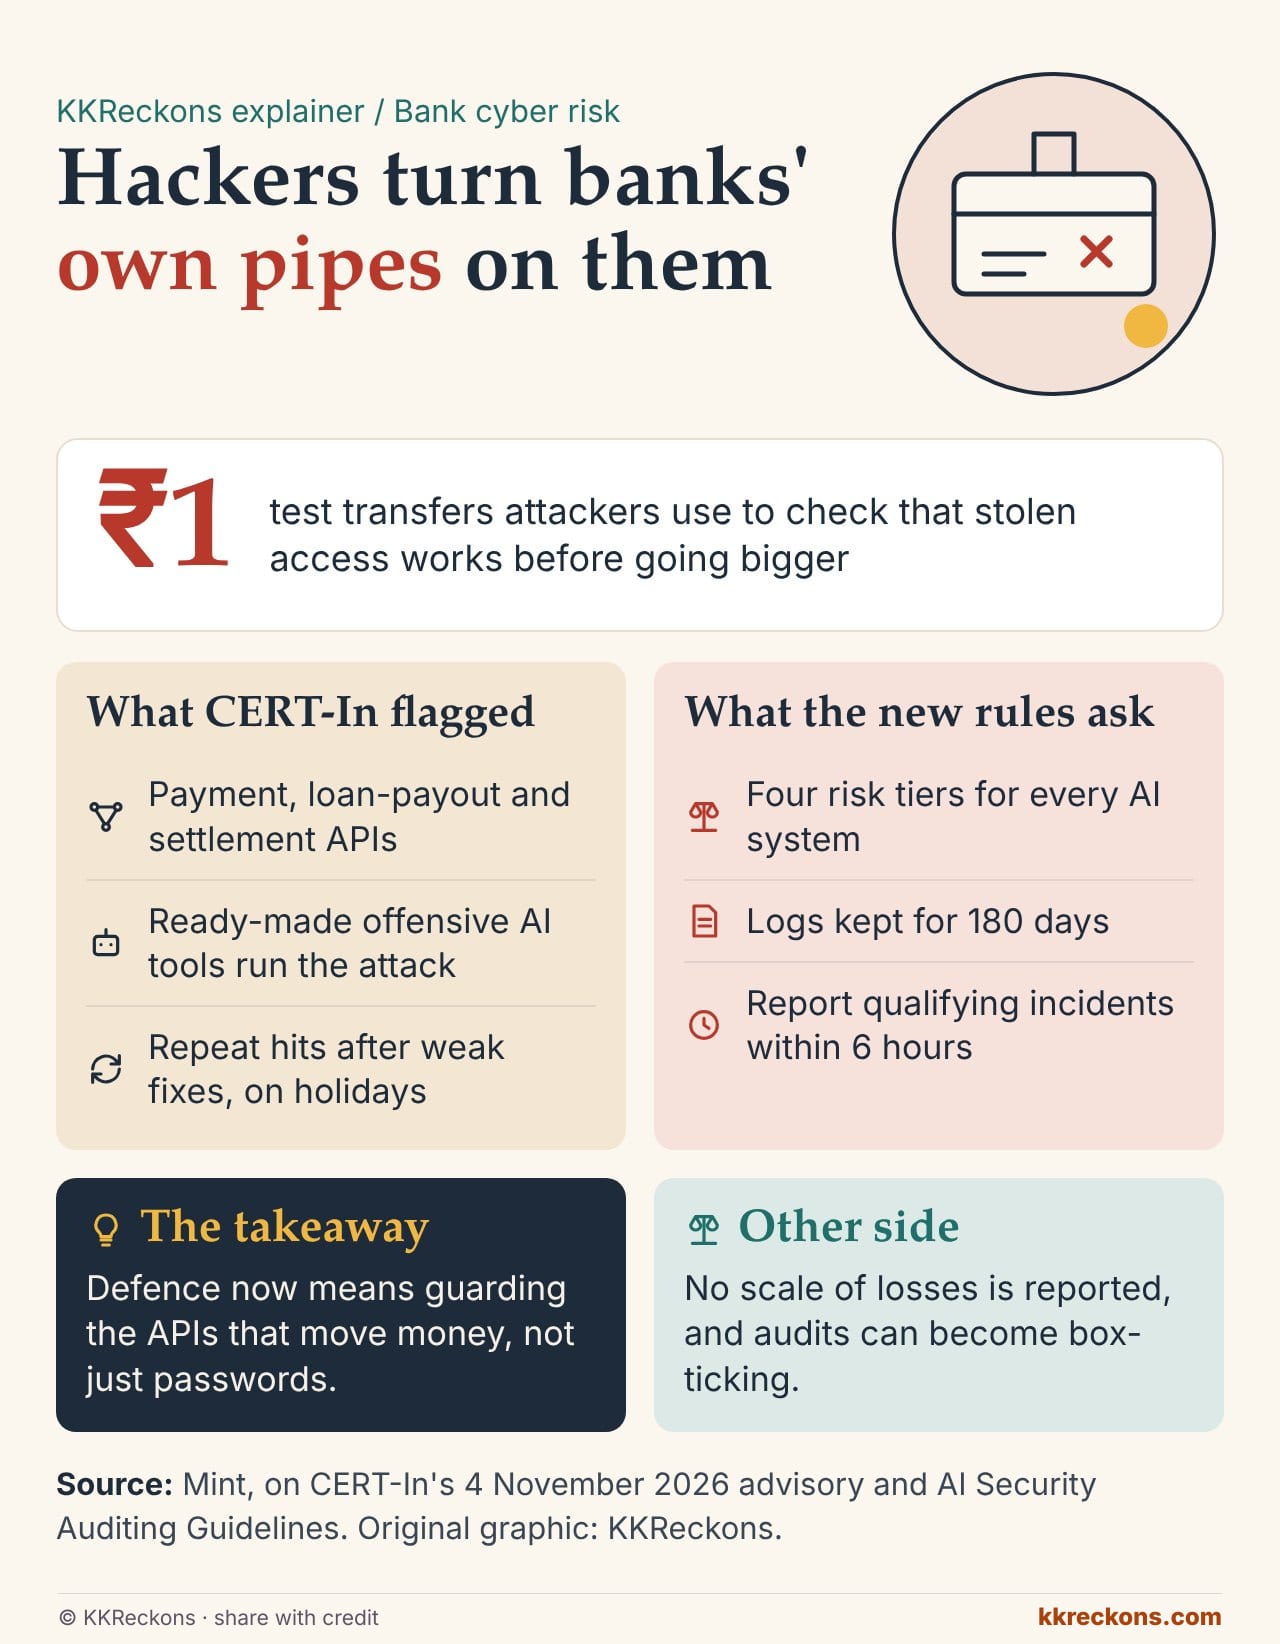
- CERT-In's 4 November advisory rates a campaign by an AI-assisted group it calls "Crafty Falcon" as critical. Targets include banks, NBFC Non-bank finance company: a lender that isn't a bank, such as Bajaj Finance, regulated more lightly by the RBI., digital lenders, payment aggregators and crypto exchanges.
- Attackers use publicly available offensive AI tools to probe payment, loan-disbursal and settlement APIs, test stolen access with transfers as small as ₹1, rotate IP addresses and return where fixes were incomplete, often on holidays.
- New 107-page AI Security Auditing Guidelines sort AI systems into four risk tiers, require 180-day log retention and want qualifying incidents reported within six hours.
- ₹1
- test transfers before bigger thefts
- 6 hrs
- to report qualifying incidents
Why it matters The weak spot is moving from a customer's phished password to the institution's own money-moving plumbing. The audit rules turn AI security into a recurring compliance cost that smaller NBFCs and fintechs will feel most; customers' best defence remains 2FA and never sharing OTPs.
Other side Advisories exist to sound alarms, and Mint reports no tally of losses. Experts it quotes warn that rules alone won't help unless banks build their own security teams, or audits risk becoming box-ticking.