Binance says fake job interviews opened the door to its $6.3bn heist (opens the source in a new tab)
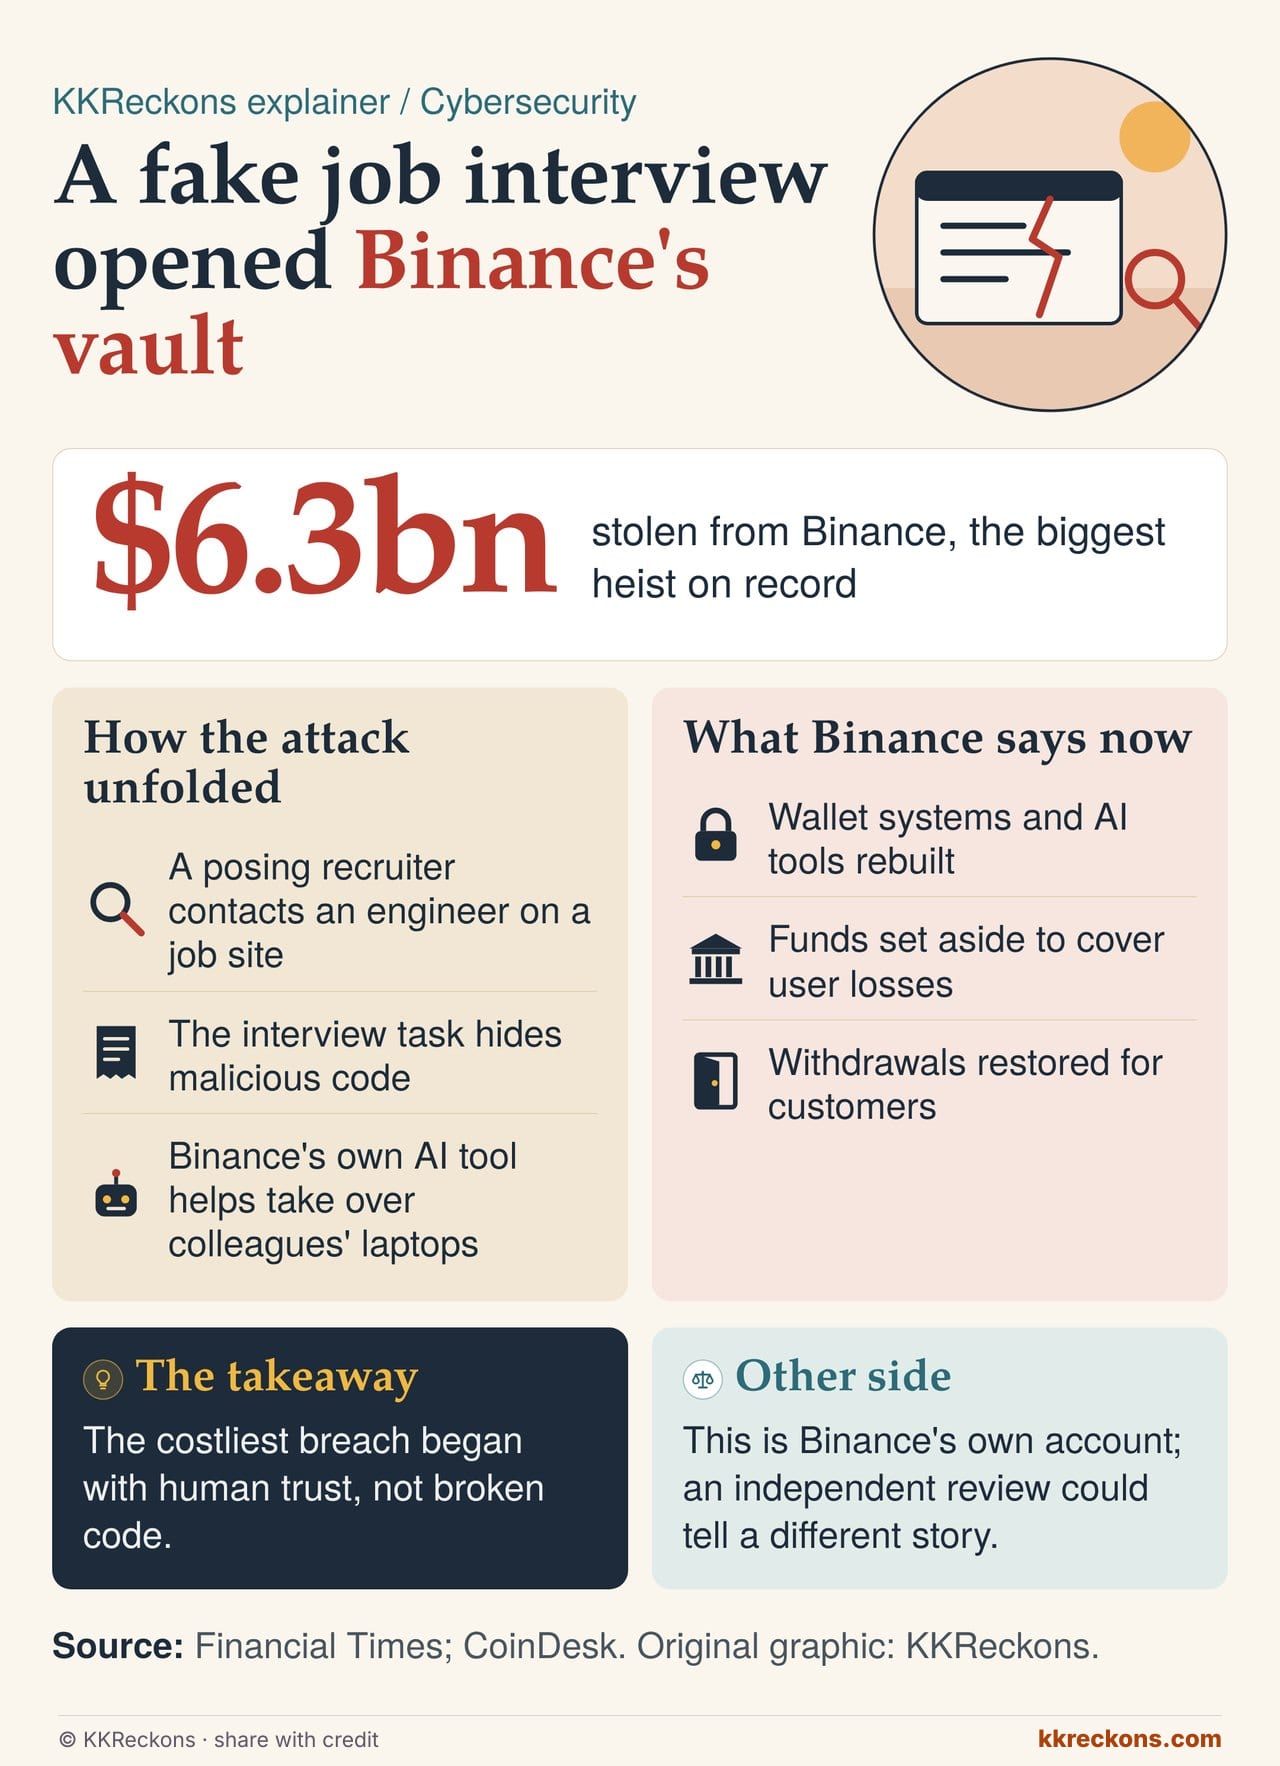
- Binance's own investigation says the thieves behind last week's theft, which the FBI blames on the North Korea-linked group TraderTraitor, posed as recruiters and gave an engineer an interview task laced with malware.
- That foothold, plus an earlier tampered download on another engineer's laptop, let them use Binance's in-house AI tool to take over colleagues' machines and trigger the attack on 29 October.
- The exchange says it has rebuilt its wallet systems and AI tools, set aside money to cover users' losses and reopened withdrawals.
- $6.3bn
- stolen in the biggest heist on record
Why it matters The weakest point in a crypto vault was a job seeker's trust. As companies wire AI agent AI software that takes actions on its own, like booking, buying or moving money, not just answering questions. into their systems, one infected laptop can now reach much further than it used to.
Other side This is Binance describing its own breach, and it is keeping some security details private. Its account may stress the attackers' cunning over its own control gaps; an independent review would tell more.