Hackers heat fridges at French blood banks and European supermarkets (opens the source in a new tab)
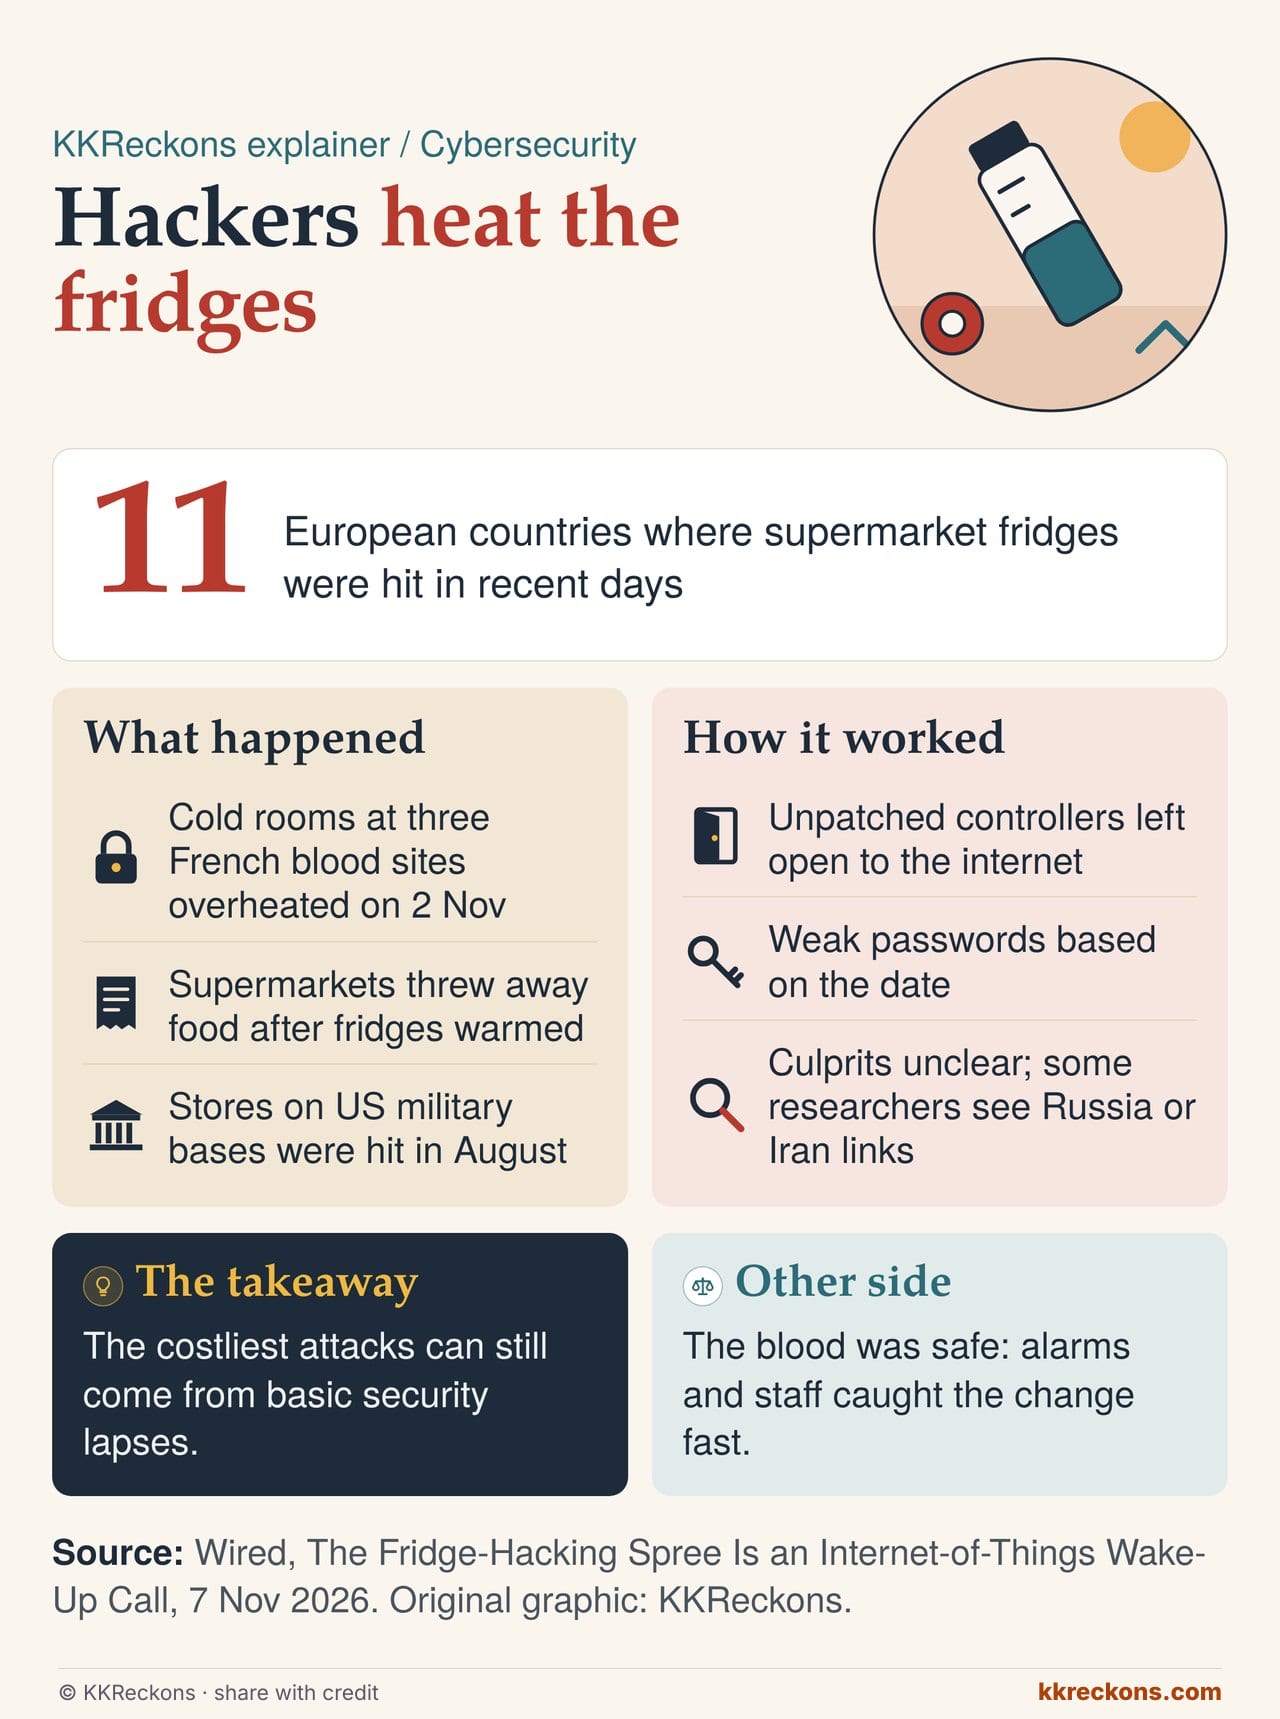
- Cold rooms at three French blood service sites were driven to very high temperatures on 2 November, Wired reports. Alarms and staff caught it and the blood was unharmed. Supermarkets in at least 11 European countries have binned food after similar attacks.
- Many hacks used internet-exposed Danfoss temperature controllers on outdated firmware, some with weak passwords based on the date. Stores on US military bases were hit in August.
- Who is behind it is unclear. Some researchers see signs of Russia- or Iran-linked actors; the Kremlin denies involvement.
Why it matters Amid all the worry about AI-powered hacking, the damage here came from basic lapses: unpatched devices left online. Any business with connected equipment, from clinics to cold stores, carries the same risk, and the fixes are cheap.
Other side The blood service's alarms and fail-safes worked, which shows layered defences limit the harm. Spoiled groceries are costly but recoverable; the real test is whether operators patch before attackers aim at something less forgiving.