Fintech body UFF drafts a code for tech vendors after cyberattacks (opens the source in a new tab)
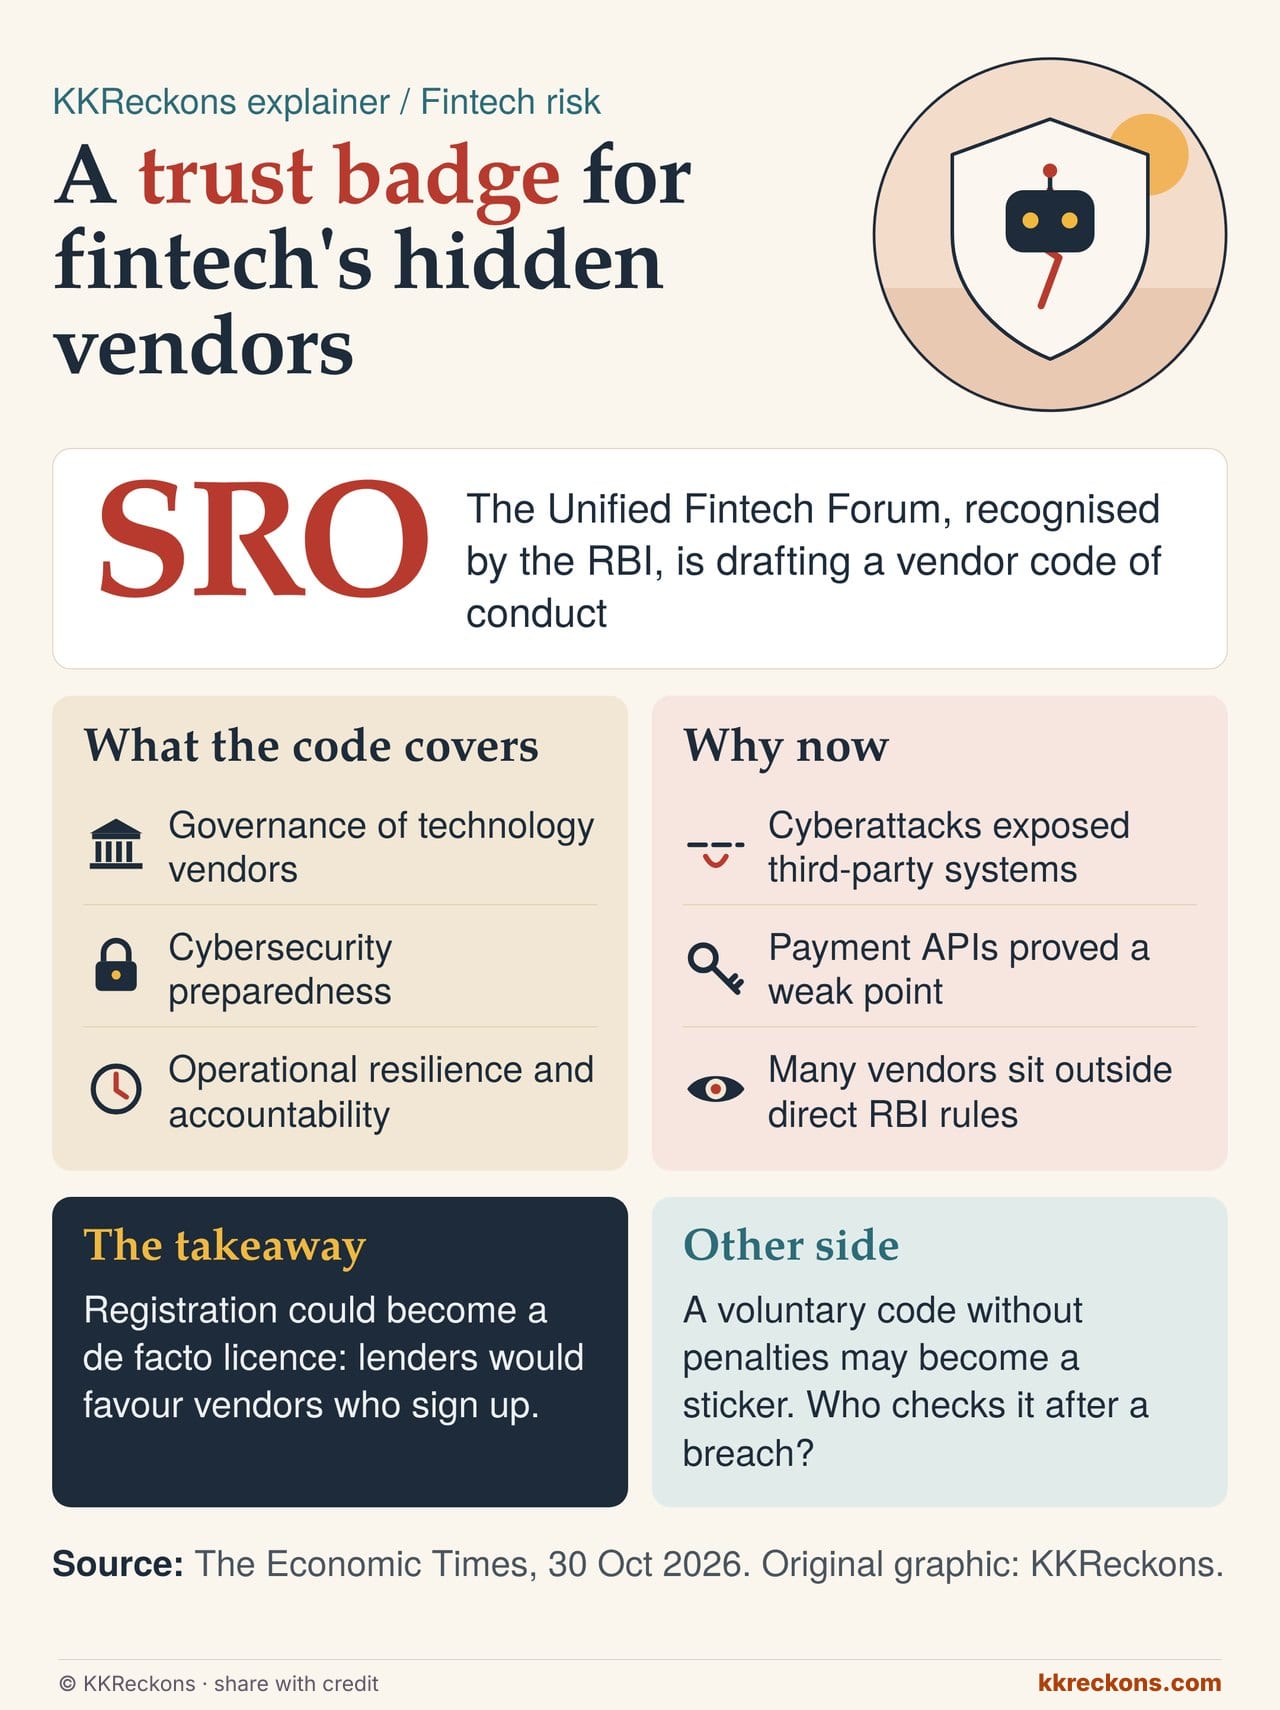
- The Unified Fintech Forum, the RBI-recognised self-regulatory body for fintechs, is drafting a code of conduct for technology and RegTech vendors covering governance, cyber readiness, resilience and accountability, ET reports.
- Fintechs and regulated lenders are likely to favour vendors that register, so sign-up could become a de facto accreditation. The trigger is a run of cyberattacks that exposed weak third-party systems and payment APIs.
- Many of these vendors run KYC, credit checks, loan systems and collections, yet are not directly regulated by the RBI.
Why it matters Lenders have outsourced the plumbing of digital credit to firms the regulator does not watch. A voluntary badge is the cheapest way to start pricing that hidden risk.
Other side A code with no penalties may become a sticker that big vendors collect and small ones struggle to afford. Who audits compliance, and what happens when a badge-holder is breached?